 HackerTube.runGood videos, with context.
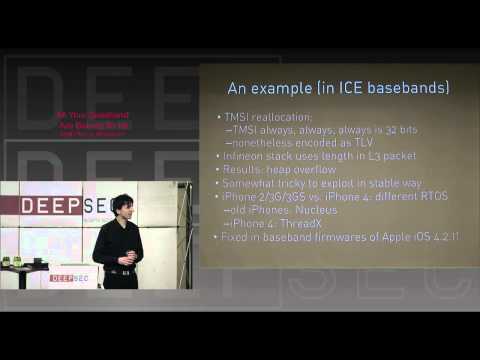
DeepSec 2010: All your baseband are belong to us by Ralf Philipp Weinmann
About this video
A DeepSec 2010 conference talk by Ralf Philipp Weinmann on attacking the baseband processor of mobile phones rather than the application processor. It covers how open-source GSM base stations make malicious-tower attacks practical against neglected GSM stacks.
Why it appears in the archive
Cited as the reference for baseband compromise, especially the point that owning the baseband can expose the application processor's memory.
AI-generated summary and labels from the source dataset; verify important details against the video. Source & credits.
From the Hacker News discussion
I really see this working remotely, as long as you have control over a cell phone tower or you use a phony portable base station, both of which are within the NSA's reach. The thing is phone baseband software (which is reused on different phone models and controls the phone's I/O including GSM, USB, etc.) has hardly ever been under attack. When the iPhone arrived with its new security model, baseband bugs became one of the major ways to jailbreak a phone. Those bugs have been fixed one by one, but they were mostly on the USB side - the GSM side has been impractical to attack. A carefully crafted GSM packet could in 2008 and probably could now cause a buffer overflow in the baseband and gain access. An interesting presentation on the topic: [VIDEO]
Read original comment ↗Only open-source apps on open-source operating systems [..] ...running on Open Source hardware. Many modern smartphones employ a baseband processor and an application processor with shared memory. While the app processor might be running an open-source compiled Android, the baseband processor is usually on a closed, not externally verified (and very buggy) RTOS provided by the manufacturer (Qualcomm, MediaTek, TI, ...)[0]. Owning the baseband is sufficient to gain access to the raw RAM of the application processor, to read any IM messages and keys, to manipulate data, code and whatever else you like. And all this is completely undetectable by any "antivirus" software running on the app processor. [0] [VIDEO]
Read original comment ↗Yes. Some further research I did since this thread started has shown that in some phones, even the microphone and camera are under the direct control of the baseband processor. In others, it's not. But in most phones, the CPU and BB share memory, which opens the door for the BB to do all sorts of nasty things to the OS on the CPU. [VIDEO]
Read original comment ↗> Do you know in which part of the phones this is supposed to be in? The baseband chip.. it runs its own RTOS (separate from Android/ios/etc): [LINK] Rather than explaining, I think this link is a pretty good example: a chip from qualcomm that was sold at least through 2012: [LINK] It was demonstrated at BlackHat in 2011 on an iPhone 4 and HTC Dream (android): [LINK] [LINK] Edit: Slides from a talk at DeepSec: [LINK] Edit: video: [VIDEO] edit: I think this is the paper: [LINK]
Read original comment ↗